
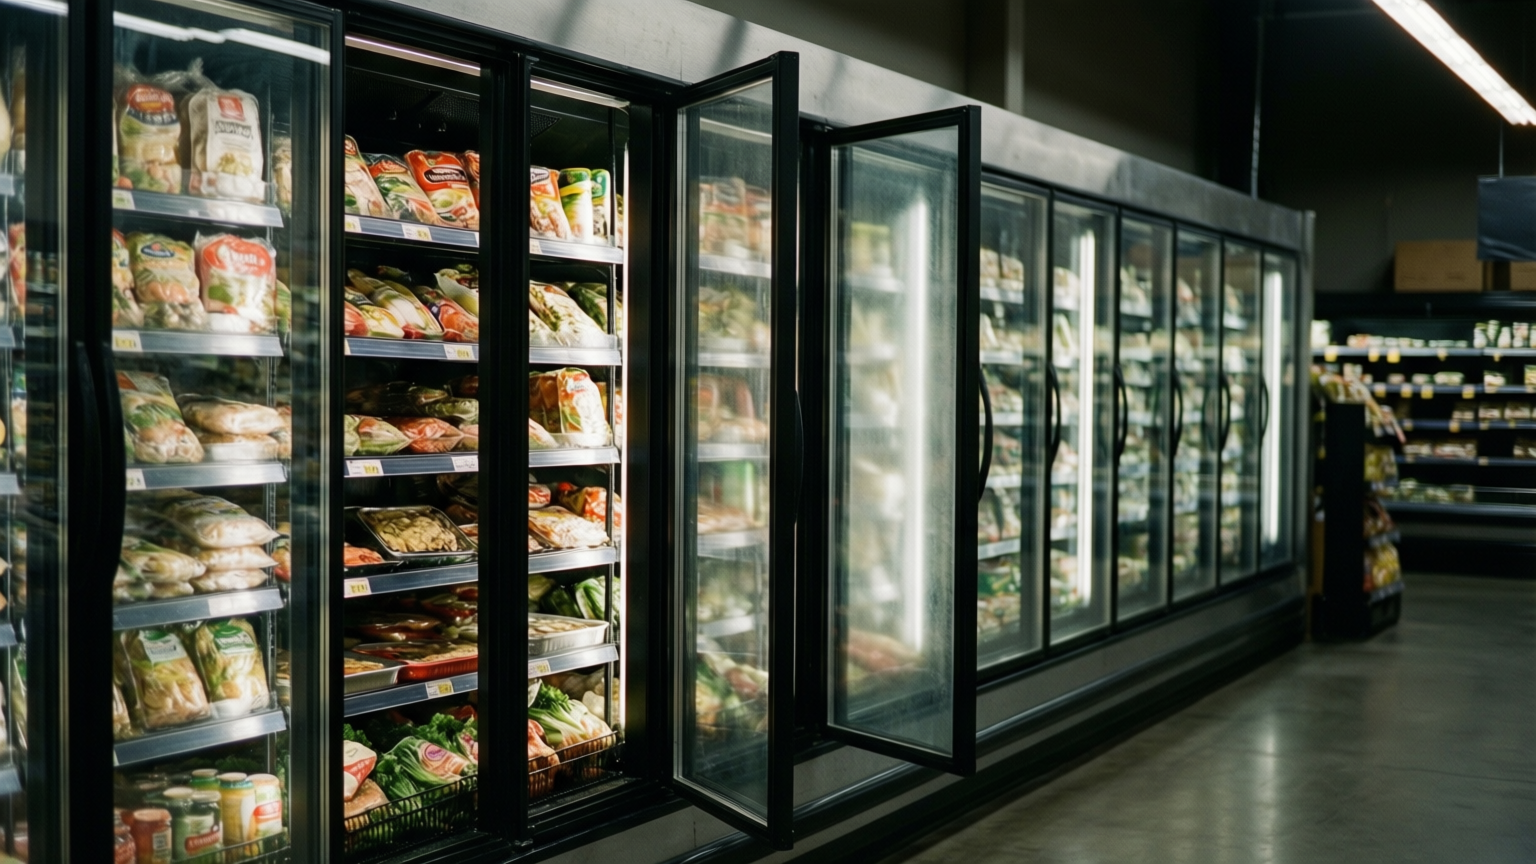
A coordinated cyberattack targeting refrigeration systems across hundreds of supermarkets in Europe has resulted in significant food spoilage and electrical fires. The incident, which primarily affected stores in France but also reached Spain, Portugal, Poland, Germany, and Belgium, highlights severe vulnerabilities in industrial internet-of-things devices. The attack compromised controllers used to manage store-wide cooling fleets, leading to catastrophic equipment failure.
Outdated Controllers Exposed to the Internet
French authorities confirmed that the systems involved were Internet-connected controllers designed for remote administration by technicians. Attackers exploited these connections to activate defrost cycles continuously, driving internal temperatures up to 50 degrees Celsius (122 degrees Fahrenheit). The resulting heat not only ruined perishable goods but also caused electrical systems to catch fire in several locations.
Security researchers identified that the compromised devices were manufactured by Danfoss of Denmark and Dixell, a brand under the US parent company Copeland. All three controller models involved contained critical vulnerabilities that allowed attackers to log in with administrative privileges. Until recently, Danfoss controllers utilized a daily changing password generated from publicly available firmware code. This method allowed anyone with the technical skill to analyze the code to replicate the password for any unpatched device across hundreds of stores.
Copeland acknowledged the issue in an email, stating that the vulnerability was identified in a discontinued, end-of-life generation of controllers. The company noted it is working with customers to prevent similar incidents. Danfoss representatives cited discontinued models as well but did not immediately respond to further questions.
Preventable Security Failures
Experts emphasize that the scale of the damage was driven by basic cybersecurity oversights. Affected stores likely failed to isolate the controllers behind a virtual private network (VPN) or restrict access to a specific list of allowed IP addresses. These measures are standard practice for industrial equipment but were absent in this case.
Researchers at Pen Test Partners stated that proper cyber hygiene would have prevented the breach. They advised taking controllers off the public internet, using VPNs for remote access, and ensuring third-party equipment is documented and patched. Security firm Claroty and the US Cybersecurity and Infrastructure and Security Agency had previously warned about these specific threats in late 2023 and early 2024, respectively.
The financial impact is estimated to be in the tens or hundreds of millions of euros. The incident underscores the tension between financial constraints and security investments in the retail sector. Many companies delay upgrading equipment until a crisis forces their hand, often realizing the cost of inaction only after a devastating event.
The identity of the attackers remains unknown, and they have not claimed responsibility. This silence raises the possibility that the motive was mass vandalism. Alternatively, it could indicate a nation-state actor aiming to create widespread disruption across the continent. The event serves as a stark reminder of the risks associated with leaving critical infrastructure exposed to the public internet.
Source: Ars Technica
